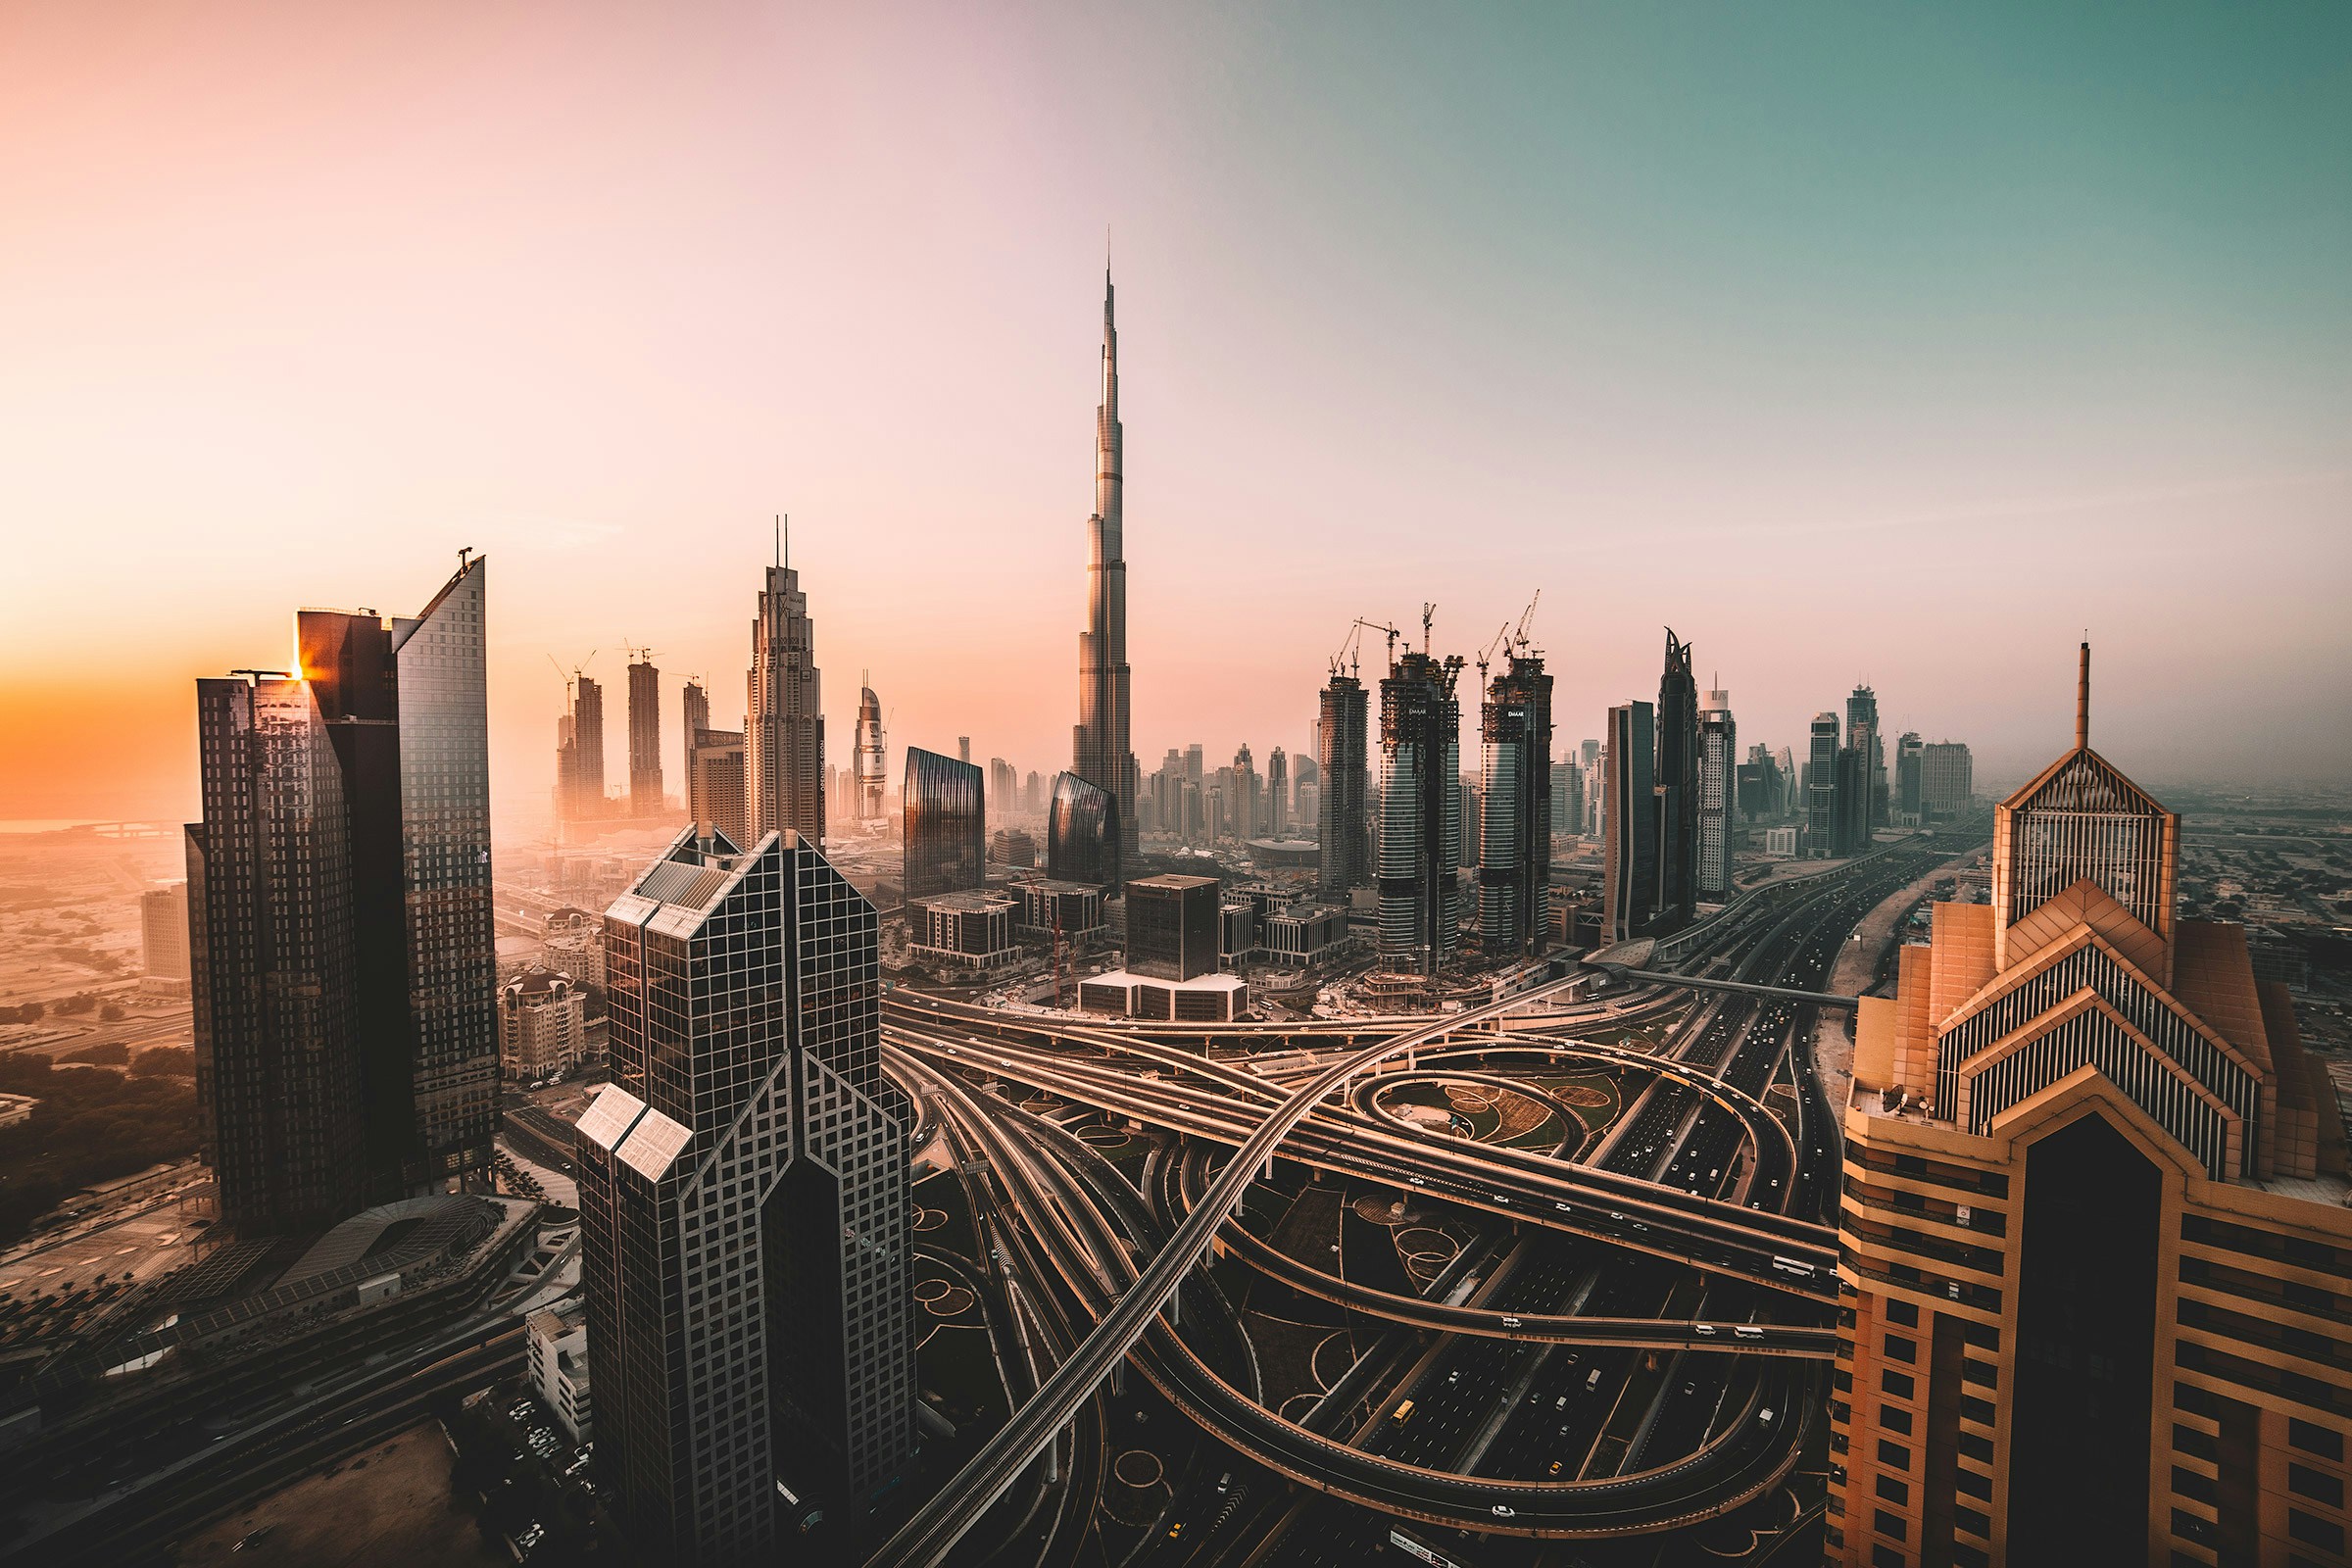
Die Vorschriften der Vereinigten Arabischen Emirate und der Golfstaaten unterscheiden sich erheblich von den europäischen Rahmenbestimmungen. Die Staaten des Golfkooperationsrates (GCC) - die Vereinigten Arabischen Emirate, Saudi-Arabien, Katar, Bahrain, Kuwait und Oman - gehören zu den am schnellsten wachsenden Telekommunikationsmärkten der Welt. Europäische Betreiber, Betreiber virtueller Netze und Technologieanbieter, die in diese Märkte eintreten oder dort Partnerschaften eingehen möchten, müssen verstehen, dass sich die Landschaft der Telekommunikationsüberwachung am Golf grundlegend von der unterscheidet, an die sie in der EU gewöhnt sind. Die Regulierungsphilosophie, die institutionellen Strukturen, die technischen Anforderungen und der Grad der staatlichen Beteiligung an der Telekommunikationsüberwachung unterscheiden sich erheblich vom europäischen Modell.
Dieser Artikel konzentriert sich in erster Linie auf die Vereinigten Arabischen Emirate als den wichtigsten Golfmarkt für internationale Betreiber, geht aber auch auf allgemeine Themen in der gesamten GCC-Region ein. Die wichtigste Erkenntnis für europäische Betreiber ist, dass der Eintritt in den Telekommunikationsmarkt der Golfregion eine gründliche Neubewertung der Annahmen darüber erfordert, wie die Telekommunikationsüberwachung funktioniert, wer sie durchführt und wie die Einhaltung in der Praxis aussieht.
Telekommunikationsüberwachung (TKÜ) in den VAE: Anforderungen für den Marktzugang
In the EU, lawful interception operates within a framework of judicial oversight, proportionality, and fundamental rights protections. Interception generally requires judicial authorisation or, for national-security interception, approval by a minister subject to independent oversight; oversight bodies review the use of surveillance powers, and operators operate within a context of legal certainty and procedural safeguards. In the Gulf states, the regulatory philosophy is markedly different. Telecommunications surveillance is generally treated as a sovereign prerogative, exercised by state security agencies with broad authority and, in most cases, limited independent oversight.
In den VAE ist die Regulierungsbehörde für Telekommunikation und digitale Verwaltung (TDRA) - früher Regulierungsbehörde für Telekommunikation (TRA) - die wichtigste Regulierungsbehörde für den Telekommunikationssektor. Die TDRA legt den Rechtsrahmen fest, innerhalb dessen die Betreiber arbeiten müssen, einschließlich der Anforderungen in Bezug auf die Telekommunikationsüberwachung. Die operative Leitung der TKÜ-Maßnahmen wird jedoch in erster Linie von den Sicherheitsdiensten bestimmt, und die Betreiber müssen bereit sein, eng mit diesen Behörden zusammenzuarbeiten, um deren Anforderungen zu erfüllen.
The UAE’s telecommunications sector is governed by Federal Decree-Law No. 3 of 2003 Regulating the Telecommunications Sector, as amended, and by the licences TDRA issues under it; the specific interception powers are not set out in a public regulation. Federal Decree-Law No. 34 of 2021 on Countering Rumours and Cybercrimes makes unauthorised interception a criminal offence. The scope of the state’s powers is significantly broader than in most EU jurisdictions, and the procedural safeguards are different in nature. The UAE has only two licensed public telecom operators (e& and du), whose licences TDRA renewed in 2026 until 2046. European entrants usually come in through a partnership or MVNO arrangement with one of them, so the LI set-up is largely the host’s.
Technische Anforderungen in den VAE
Die technischen Anforderungen für die Telekommunikationsüberwachung in den VAE werden vom TDRA in Absprache mit den Sicherheitsbehörden festgelegt. Die Betreiber sind verpflichtet, folgende Maßnahmen zu ergreifen: Überwachungsfähigkeiten that meet the TDRA’s specifications, which include the ability to intercept voice, SMS, data, and IP-based communications. The detailed technical specifications are confidential and are made available to licensees only.
One of the most significant differences from the European model is the degree of direct access that security agencies may require to an operator’s network infrastructure. Public reports suggest that in parts of the region security agencies may have more direct access to operator systems than is usual in the EU; operators should clarify the access model contractually before signing. This model contrasts sharply with the European approach, where operators typically retain control over the activation and execution of intercepts and deliver the resulting data to law enforcement through defined Übergabeschnittstellen.
UAE licensees are also subject to content and service-access rules, for example on unlicensed VoIP, which are enforced through network filtering. These are separate from lawful interception obligations. The deployment of such technologies raises significant technical and ethical questions for European operators, particularly given the EU’s emphasis on privacy and data protection.
For operators providing services in the UAE, the technical compliance requirements are non-negotiable. Failure to deploy the required interception capabilities can put the licence of the operator concerned at risk. Compliance is monitored by the regulator and the security authorities under confidential licence conditions.
GCC-Landschaft im weiteren Sinne
While each GCC state has its own regulatory framework, several common themes emerge across the region. Saudi Arabia’s Communications, Space and Technology Commission (CST) licenses operators whose obligations include cooperation with the security authorities; the detailed requirements are not public.
Qatar’s Communications Regulatory Authority (CRA) and Bahrain’s Telecommunications Regulatory Authority (TRA) likewise require licensees to cooperate with the security services. In Kuwait and Oman, the regulatory frameworks are somewhat less publicly documented, but the expectation of operator cooperation with interception requirements is consistent across the region.
A common feature across the GCC is tight control of OTT services. The Gulf states have at various times restricted or blocked VoIP services such as WhatsApp voice calls, Skype, and FaceTime, partly for commercial reasons (to protect the revenues of incumbent operators) and partly for security reasons (to maintain surveillance capabilities). Operators entering the GCC market must understand these dynamics and be prepared to comply with requirements that may include the blocking or filtering of specific services.
Herausforderungen für europäische Betreiber
European operators entering the Gulf market face several significant challenges related to lawful interception. The first is the tension between the Gulf’s surveillance requirements and the EU’s legal framework for data protection and privacy. Operators subject to the GDPR may find themselves in a position where compliance with Gulf interception requirements could conflict with their obligations under EU law. A conflict arises mainly where an EU-established entity or EU-hosted systems would process the data: under Art. 48 GDPR, a third-country authority’s request alone does not legitimise a transfer. Keeping Gulf LI systems and data in-country, run by the local entity, avoids most of this tension.
The second challenge is the possibility that security agencies require more direct access to the network than European operators are used to. Clarify the access model contractually and reflect it in network design, security architecture and internal governance.
The third challenge relates to scope. Content and service-access rules, such as blocking unlicensed VoIP, may require network filtering capabilities that European operators do not use at home; these are separate from LI obligations and need their own legal and export-control review.
A fourth challenge is the lack of public documentation for some aspects of the interception requirements. While the TDRA and other Gulf regulators publish general frameworks and guidelines, the detailed technical specifications for interception are often provided on a confidential basis to licensed operators. This means that operators cannot fully assess the technical requirements before entering the market and must be prepared for an iterative process of specification review, development, and testing once they have agreed their arrangement with the host licensee.
Exportkontrolle und ethische Erwägungen
European operators and technology vendors must also consider the export control implications of deploying surveillance technology in the Gulf. The EU’s Dual-Use Regulation (Regulation 2021/821) imposes export controls on certain surveillance and interception technologies, including equipment and software that could be used for the interception of telecommunications, and a catch-all for non-listed cyber-surveillance items where there is a risk of serious human rights violations (Art. 5). Operators and vendors exporting such technologies to Gulf states must ensure that they obtain the necessary export licences and comply with the conditions attached to those licences; for a German exporter the licensing authority is BAFA.
Neben der Einhaltung von Gesetzen gibt es auch ethische Überlegungen, mit denen sich die europäischen Betreiber auseinandersetzen müssen. Die Menschenrechtslage in den Golfstaaten ist Gegenstand internationaler Untersuchungen, und der Einsatz von Überwachungstechnologien in diesen Märkten birgt Reputationsrisiken. Die Betreiber sollten vor dem Markteintritt eine Due-Diligence-Prüfung in Bezug auf die Menschenrechte durchführen und Richtlinien für den Fall festlegen, dass ihre Technologie in einer Weise eingesetzt wird, die mit internationalen Menschenrechtsstandards in Konflikt steht.
Mehrere europäische Unternehmen sind im Zusammenhang mit dem Verkauf oder Einsatz von Überwachungstechnologie in der Golfregion und im Nahen Osten mit öffentlicher Kritik und rechtlichen Herausforderungen konfrontiert worden. Unternehmen, die in diesem Bereich tätig sind, sollten sicherstellen, dass sie über solide Compliance-Programme verfügen, einschließlich ethischer Überprüfungsprozesse, Schutz von Hinweisgebern und regelmäßiger Bewertungen der Auswirkungen ihrer Aktivitäten auf die Menschenrechte.
Praktische Empfehlungen
Europäischen Betreibern, die einen Markteintritt in die VAE oder einen breiteren GCC-Markt erwägen, werden mehrere praktische Schritte empfohlen. Führen Sie zunächst eine gründliche rechtliche und regulatorische Bewertung des Zielmarktes durch, einschließlich der Anforderungen an die Überwachung, der Verpflichtungen zur Datenlokalisierung und möglicher Konflikte mit dem EU-Recht. Beauftragen Sie einen lokalen Rechtsberater mit Fachkenntnissen im Bereich der Telekommunikationsvorschriften und des nationalen Sicherheitsrechts.
Zweitens: Setzen Sie sich frühzeitig im Planungsprozess mit der zuständigen Regulierungsbehörde in Verbindung, um die technischen Spezifikationen für die Telekommunikationsüberwachung zu verstehen und den Prozess der Einhaltung der Vorschriften einzuleiten. Planen Sie ausreichend Zeit für die technische Entwicklung und Erprobung ein, da die Anforderungen möglicherweise umfangreicher sind als erwartet. Drittens sollten Sie die Auswirkungen des Einsatzes von Überwachungstechnologie auf die Ausfuhrkontrolle prüfen und die erforderlichen Genehmigungen einholen, bevor Sie fortfahren.
Viertens: Führen Sie eine Menschenrechtsverträglichkeitsprüfung durch und legen Sie Richtlinien und Verfahren für den Umgang mit den ethischen Dimensionen des Einsatzes von Überwachungstechnologie in der Golfregion fest. Fünftens: Stellen Sie sicher, dass Ihre Corporate-Governance-Strukturen eine angemessene Überwachung von Überwachungsaktivitäten ermöglichen und dass Ihre internen Richtlinien sowohl mit den lokalen rechtlichen Anforderungen als auch mit den ethischen Standards Ihrer Organisation übereinstimmen.
Schlussfolgerung
The UAE and the broader GCC present significant opportunities for European telecommunications operators, but the lawful interception landscape in these markets requires a fundamentally different approach from what operators are accustomed to in Europe. The state-centric regulatory philosophy, the broad scope of interception powers, the possibility of direct agency access, and the ethical considerations associated with surveillance in the Gulf all demand careful preparation, specialist expertise, and a proactive approach to compliance. Operators that invest in understanding these requirements and building appropriate capabilities will be well positioned to succeed in these dynamic and growing markets, while managing the legal, technical, and reputational risks that come with operating in a fundamentally different regulatory environment.
Das rechtliche Umfeld der VAE unterscheidet sich erheblich von den europäischen Normen. Betreiber, die den Markteintritt planen, müssen die Anforderungen an die gesetzliche Überwachung in den Vereinigten Arabischen Emiraten genau verstehen, bevor sie sich zum Einsatz verpflichten.
Verwandte Artikel
Weitere Informationen zu verwandten Themen finden Sie in diesen Artikeln:
- LI Requirements in the Netherlands: Telecommunicatiewet Chapter 13, ETSI-IP.nl and What MVNOs Must Know
- Spaniens Anforderungen an TKÜ-Maßnahmen nach dem LGTEL
- Lawful Interception über Satellit: Warum MNO-Satellitenpartnerschaften neue Compliance-Anforderungen stellen
Externe Ressourcen
Die folgenden externen Quellen bieten zusätzlichen Kontext und offizielle Dokumentation: