합법적 감청을 위한 심층 패킷 분석 이는 대개 법 집행 측면과 연관되어 있습니다. 즉, 해당 기관은 원시 IP 패킷을 수신하여 자체 모니터링 시설에서 이를 분석합니다. 그러나 점점 더 많은 네트워크 사업자와 기관들이 이 업무 중 일부를 서비스 제공처에서, 트래픽과 가까운 곳에서. 이 모델에서 서비스 제공자는 데이터가 차단되는 지점에서 메타데이터를 추출하고 보강한 뒤, 통신 내용의 전체 사본과 함께 이를 전달합니다.
Whether a provider may do any of this depends on national law: in Germany, analysis stays with the agency. Where it is allowed and done right, provider-side DPI speeds up investigations, can reduce data volumes where an order limits the scope, and gives agencies context they could not reconstruct themselves. Done wrong, it breaks evidence rules or exceeds the legal mandate. This article explains the architecture, what can be extracted, how enriched data is delivered, and where the boundaries are.
주요 내용
- 프로바이더 측 DPI 보완 요소 해당 통지의 전문. 명령 및 국내 규정에 명시적으로 적용 범위를 축소할 수 있도록 허용된 경우가 아닌 한, 이는 원본을 대체할 수 없다.
- 해당 제공업체는 network context the agency lacks: line identity, NAT mappings, cell and location data, device identifiers and precise session timing. Subscriber details such as name and address need a separate request.
- 일반적으로 추출되는 메타데이터에는 다음이 포함됩니다. 트래픽 기록, DNS, SNI, TLS 지문(JA4), 애플리케이션 분류, VoIP 신호 및 활동 유형.
- 보강된 데이터는 다음 형식으로 제공되어야 합니다. 합의된, 문서화된 형식, for example as additional IRI records where the national specification allows it. Whether a provider may deliver any of it is jurisdiction-dependent: in Germany the provider hands over only the copy and the § 7 TKÜV event data, and analysis belongs to the agency.
- Where national law allows it, everything must be target-specific, reproducible, documented and strictly separated from commercial DPI. An acceptance concept documents it but cannot make it lawful.
왜 서비스 제공자 측에서 심층 패킷 검사를 수행해야 할까요?
| 운전자 | 대행사에게 주는 이점 | 제공자에게 주는 혜택 |
|---|---|---|
| 대역폭 증가 (멀티 기가비트 FTTH, 5G) | 전체 사본을 처리하는 데 시간이 걸리더라도 메타데이터는 즉시 확인할 수 있습니다. | 범위 제한이 적용되는 인계 구간에서의 부담이 줄어듦 |
| 암호화된 트래픽 | 사전 분류된 세션 및 지문 | 기존 DPI 전문 지식의 재활용 |
| 네트워크 컨텍스트 | Line, NAT, cell and device data attached to each flow | Fewer follow-up requests for basic context, where national rules list the data for the copy (subscriber name and address always need a separate request) |
| 시급한 사례 | 활동 패턴에 대한 준실시간 알림 | 명확하게 정의된 자동화 프로세스 |
| 복잡한 접근 모델 | CGNAT 및 도매 환경에서의 올바른 출처 표기 | 불완전한 감청 기록에 대한 분쟁이 줄어들었다 |
법이 그어 놓은 경계선
무언가를 설계하기 전에, 서비스 제공자는 자신의 법적 지위를 명확히 파악해야 합니다:
- 먼저 전문을 소개합니다. In most European jurisdictions the provider must deliver a 완전하고 수정되지 않은 사본 of the target’s telecommunications. Where national law allows enrichment, it is an addition; in Germany it is not allowed (see below). Filtering is allowed only where the order limits the scope.
- 주문 내용 이외의 분석은 없습니다. 프로바이더 측 DPI는 다음의 트래픽만 처리할 수 있습니다. 정렬된 대상 그리고 오직 감청 목적에 한해서만 허용됩니다. 대량 분석이나 비표적 분석은 허용되지 않습니다.
- 상업용 DPI와의 분리. EU 개방형 인터넷 규정 (EU) 2015/2120은 트래픽 관리를 위한 DPI를 제한하지만, EU 또는 국내법을 준수하기 위해 필요한 조치는 허용하고 있습니다. 따라서 LI 처리는 별도의 접근 제어 환경에서 수행되어야 하며, 어떠한 경우에도 상업용 시스템에 데이터를 제공해서는 안 됩니다.
- 기밀 유지. 직원과 시스템은 통신 비밀 유지 의무를 준수해야 하며, 가입자는 해당 조치를 눈치채지 못해야 합니다.
- Germany is stricter. The obliged provider must enable the measure (§ 100a(4) StPO) and hand over a complete copy plus the event data listed in § 7 TKÜV, and nothing else at the handover point (§ 8(2) No. 2 TKÜV). Analysis of the content, including DPI classification, belongs to the agency. A BNetzA acceptance cannot create a legal basis for extra processing. Provider-side enrichment is only an option where national law expressly provides for it.
참조 아키텍처
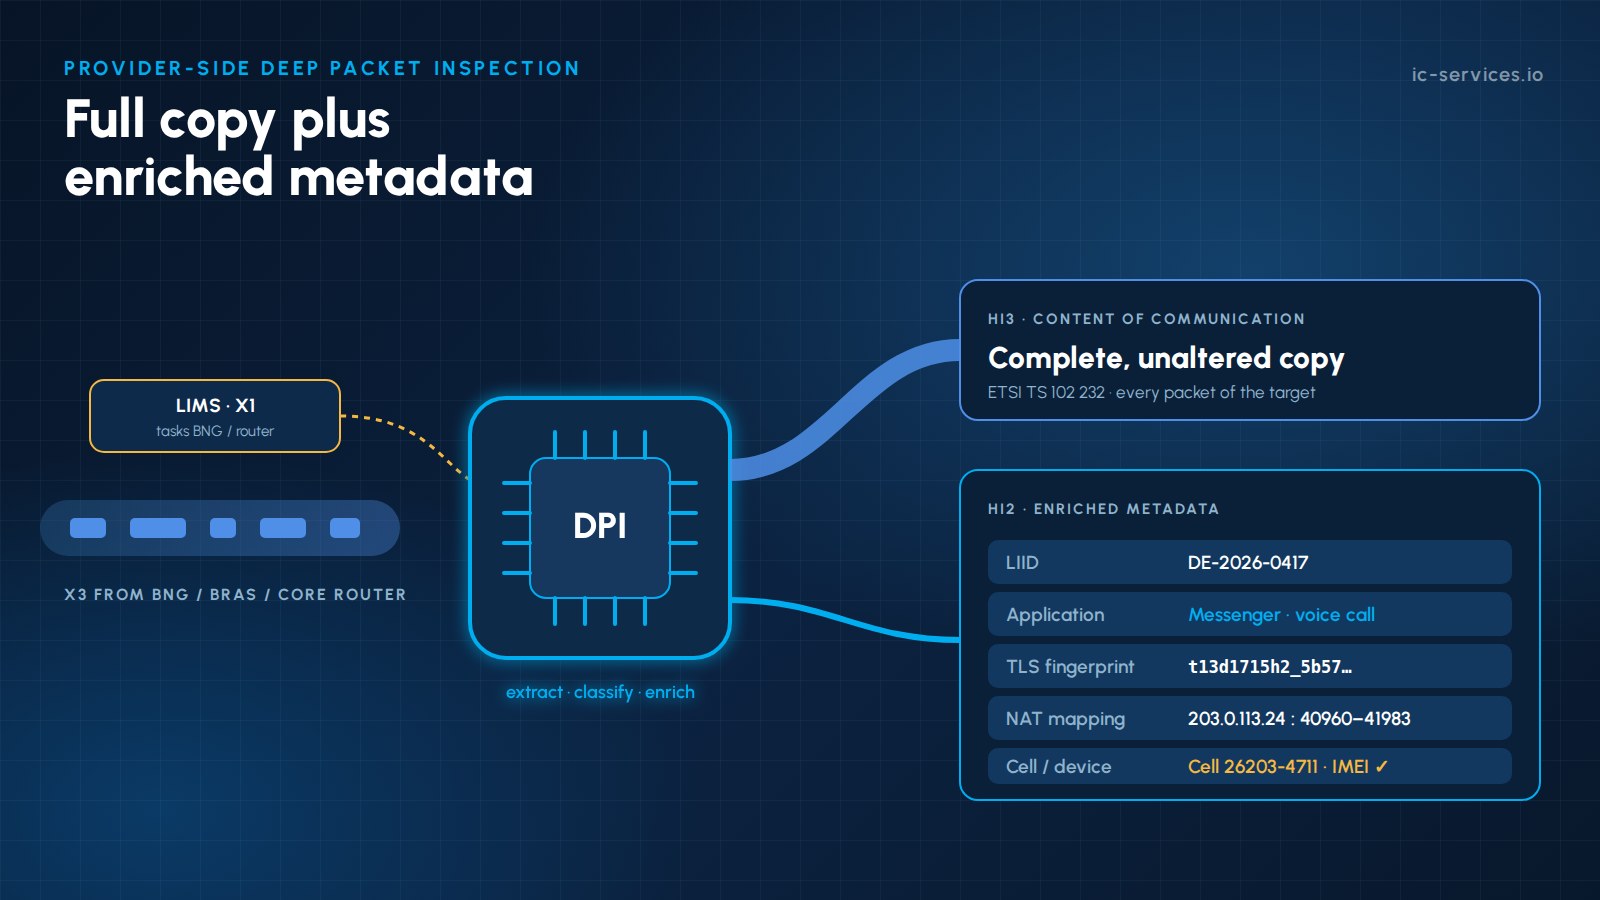
- 교통 접근성: BNG/BRAS for PPPoE and IPoE access, and PE or core routers for fixed-IP lines, copy the target’s traffic with their built-in LI function, using ETSI TS 103 221 (X1 tasking, X2/X3 delivery) where supported or the vendor’s LI interface. The ADMF handles the tasking, and the mediation layer converts the delivered streams into the ETSI handover format. Optical TAPs or virtual mirror ports are only a fallback where no native LI function is available.
- 목표 발동: LIMS/ADMF가 대상을 활성화하면, RADIUS/Diameter, DHCP 또는 패킷 게이트웨이에서 전송된 세션 이벤트를 통해 DPI 노드에 현재 대상에 속한 IP 주소와 접두사가 무엇인지 알려줍니다.
- 특정 대상을 대상으로 하는 심층 패킷 검사 노드: 해당 노드는 정렬된 대상의 X3 스트림만 처리합니다. 10/40/100 Gbit/s 속도의 고성능 패킷 처리(예: DPDK 또는 FPGA 기반 NIC)를 통해 플로우를 재조립하고, 프로토콜을 식별하며, 메타데이터를 추출합니다.
- 심화 학습: each flow is tagged with the LIID, the target identifier, the NAT mapping (public IP and port block), cell ID or location, and the IMEI where available. Enrichment is limited to data the national rules list for the copy; subscriber details such as name and address still require a separate information request.
- 중재 및 이행: the full copy is delivered as CC via HI3, according to ETSI TS 102 232-3 or -4 for fixed access, or 3GPP TS 33.108/33.128 over TS 102 232-7 for mobile, and any enriched metadata permitted by national law is delivered via HI2.
- 감사 및 보존: DPI 출력 데이터는 전송에 필요한 기간 동안만 보관되며, 모든 구성 및 서명 버전이 기록됩니다.
참조 X1/X2/X3 인터페이스 및 중재 함수의 작동 원리 기본이 되는 인터페이스에 대해서는.
무엇을 추출하고 농축할 수 있나요?
| 메타데이터 | 출처 | 수사에 대한 가치 |
|---|---|---|
| 흐름 기록 (5-튜플, 시작/종료, 바이트, 패킷) | 패킷 헤더 | 활동 전체 개요 |
| DNS 쿼리 및 응답 | 암호화되지 않은 DNS | 사용된 서비스 및 도메인 |
| TLS SNI, ALPN, JA4 / JA4S 지문 (JA4S에 대한 FoxIO 라이선스 약관을 참고하십시오) | TLS/QUIC 핸드셰이크 | 애플리케이션 및 기기 식별 |
| 애플리케이션 분류 | DPI 서명 및 동작 | 메신저, VoIP, 스트리밍, VPN, Tor |
| 활동 유형 | 패킷 크기와 타이밍 패턴 | 메시지 vs 통화 vs 파일 전송 |
| VoIP 신호 전송 (SIP, RTP 매개변수) | 암호화되지 않은 VoIP | 참가자 및 통화 시간을 포함한 타사 VoIP 통화 |
| HTTP 호스트 및 사용자 에이전트 | 암호화되지 않은 HTTP | 서비스 및 클라이언트 소프트웨어 |
| NAT 매핑 | CGNAT 로그 | 공용 IP와 포트, 그리고 대상 간의 연결 |
| 위치 및 기기 | 셀 ID, IMEI, 접속 회선 | 어떤 장소에서, 어떤 기기를 통해 활동이 발생했는지 |
Which of these an access provider may deliver depends on national law. In Germany, classification and service-level reconstruction of third-party services are done by the agency, not the access provider. The encryption rule applies here as well: the provider removes only the encryption it applied itself. End-to-end encrypted content remains encrypted, and the metadata above is extracted without decrypting it.
가공된 데이터 전달
There is no single, universal ETSI record type for “DPI results”. Flow summaries are standardised in ETSI TS 102 232-3 (Packet Data Summary Reporting); application classification is not. In practice, three models are used:
- 추가 IRI 레코드: extracted events (for example a detected VoIP call or an application session) are sent via HI2, using standard fields where possible, and national extensions only where the national specification provides for them.
- Flow-level IRI: where flow-level IRI is required by the warrant, ETSI TS 102 232-3 already defines it (Packet Data Summary Reporting, IPIRIOnly). Proprietary analytics streams outside the national handover specification are not permitted in Germany and need an explicit legal basis elsewhere.
- 서비스 수준 기록: 일부 관할권에서는, 명시적으로 요구되는 경우에만, 제공자는 메시징 및 멀티미디어 제공자가 자체 서비스에 사용하는 ETSI TS 102 232의 서비스별 부분과 유사하게 서비스 수준에서 이벤트를 전달합니다.
어떤 모델이든, 형식은 반드시 문서화, 버전 관리 및 합의 완료 수신 기관 및 규제 당국과 협력해야 하며, 해당 기관은 항상 완전한 사본과 대조하여 보강된 데이터를 확인할 수 있어야 합니다.
증거의 질: 보강 분석의 재현성 확보
- 다음 내용을 기록하십시오. DPI 엔진 및 서명 버전 모든 결과에 적용됩니다.
- 사용 동기화된 고정밀 타임스탬프 메타데이터가 CC 및 HI2 기록과 일치하도록 하기 위해.
- 제공 신뢰 지표 행동 분류를 위해.
- ~을(를) 유지하세요 완전한 감사 추적이력 대상 활성화, 구성 변경 및 전달과 관련하여.
- 다음과 같이 정기적으로 테스트하십시오. 기준 트래픽 서명 업데이트 후 발생하는 회귀 현상을 감지하기 위해.
서비스 제공자를 위한 이행 체크리스트
- 법적 평가: 국가 차원의 법적 체계가 허용하는 사항과 명령이 일반적으로 다루는 내용
- Where national law provides for enrichment: scope and delivery format agreed with the agencies and documented in the acceptance concept
- LIMS/ADMF에 의해 유도되는 표적 특이적 활성화만 발생
- 최대 가입자 수에 맞춰 조정된 하드웨어 가속 DPI
- AAA, DHCP, CGNAT 로그, 패킷 코어 및 위치 데이터와의 통합
- 상업용 DPI 및 트래픽 관리와의 엄격한 분리
- 버전 관리, 참조 테스트 및 감사 로그 기록
- 버퍼링 및 모니터링을 통한 안정적인 전송
ICS가 공급자 측 심층 패킷 검사(DPI)에 어떻게 도움이 되는가
ICS International Carrier Services builds on more than 20 years of team experience in telecommunications, lawful interception and compliance and on BNetzA-accepted LI implementations. We integrate network elements via their vendor LI interfaces or ETSI TS 103 221 X1/X2/X3 and operate mediation for providers today, so we know both the network and the receiving side.
- 건축 및 법률·기술적 설계 프로바이더 측 DPI(참조: 네트워크 사업자를 위한 DPI) 귀사의 국가별 체계와 승인 개념에 부합하는 것.
- 타깃 기반 DPI 및 데이터 보강 파이프라인 RADIUS/Diameter, CGNAT 로깅 및 패킷 코어 이벤트와 통합되었습니다.
- Network element integration with BNG/BRAS and core routers via their vendor LI interfaces or ETSI TS 103 221 X1/X3, plus passive probes or cloud mirroring where no native LI function is available.
- 중재 및 ETSI 업무 이관 저희를 통해 LI 미디에이션 플랫폼 및 LIMS.
- 운영 관리 24시간 내내. 참조 관리형 LI 운영.
- 맞춤형 개발 추출기, 분류기 및 전달 형식에 관해. 참조: 통합 및 사용자 지정 개발.
ICS에 문의해 주세요 귀사의 네트워크에 제공자 측 데이터 보강이 적합한지 논의하기 위해.
자주 묻는 질문
합법적 감청을 위해 심층 패킷 분석이 허용되나요?
Only where national law expressly provides for it. In Germany the provider must hand over a complete copy plus the event data listed in § 7 TKÜV and nothing else at the handover point (§ 8(2) No. 2 TKÜV); analysis of the content, including DPI classification, belongs to the agency, and a BNetzA acceptance cannot create a legal basis for extra processing. Untargeted or commercial use of LI data is never allowed.
프로바이더 측 DPI가 통신 내용의 전체 사본을 대체하나요?
아닙니다. 대부분의 관할권에서 정보 제공자는 대상자의 통신 내용을 완전하고 변조되지 않은 상태로 제공해야 합니다. 명령에서 그 범위를 명시적으로 제한하지 않는 한, DPI 기반의 메타데이터는 이에 추가로 제공됩니다.
인터넷 서비스 제공업체(ISP)가 대상자의 HTTPS 또는 메신저 트래픽을 복호화할 수 있나요?
아닙니다. 서비스 제공업체는 자사 네트워크 내에서 직접 적용한 암호화만 해제합니다. 종단 간 암호화나 애플리케이션 수준 암호화는 그대로 유지됩니다. DPI는 암호화되지 않은 헤더, 핸드셰이크 및 트래픽 패턴을 분석합니다.
DPI 메타데이터는 법 집행 기관에 어떻게 전달되나요?
Where national law allows it, as additional IRI records via HI2, using standard records such as the Packet Data Summary Reporting of ETSI TS 102 232-3 where possible. Separate analytics streams outside the national handover specification are not permitted in Germany. The format must be documented and agreed with the agencies and the regulator.
프로바이더 측 DPI와 LEA 측 DPI의 차이점은 무엇인가요?
LEA-side DPI analyses the delivered traffic in the monitoring facility. Provider-side DPI runs at the point of interception, where, if national law allows it, it can add network context such as the line identifier, NAT mappings and location, and deliver results in near real time.
관련 기사
- 중재 기능의 작동 방식 네트워크와 법 집행 기관 사이의 가교 역할
- 암호화된 DNS(DoH/DoT)와 합법적 감청 기능에 미치는 영향
- 5G SA 환경에서의 네트워크 슬라이싱: LI 타겟팅을 어떻게 복잡하게 만들며(그리고 어떻게 단순화할 수 있는가)
- AI 지원 LI: 자동화가 운영자와 법 집행 업무 흐름에 미치는 의미