
DPI FOR LAWFUL INTERCEPTION
Deep Packet Inspection for Lawful Interception
Encrypted traffic still tells a story. ICS applies DPI where it helps most: in the agency’s monitoring facility and at the operator’s point of interception.
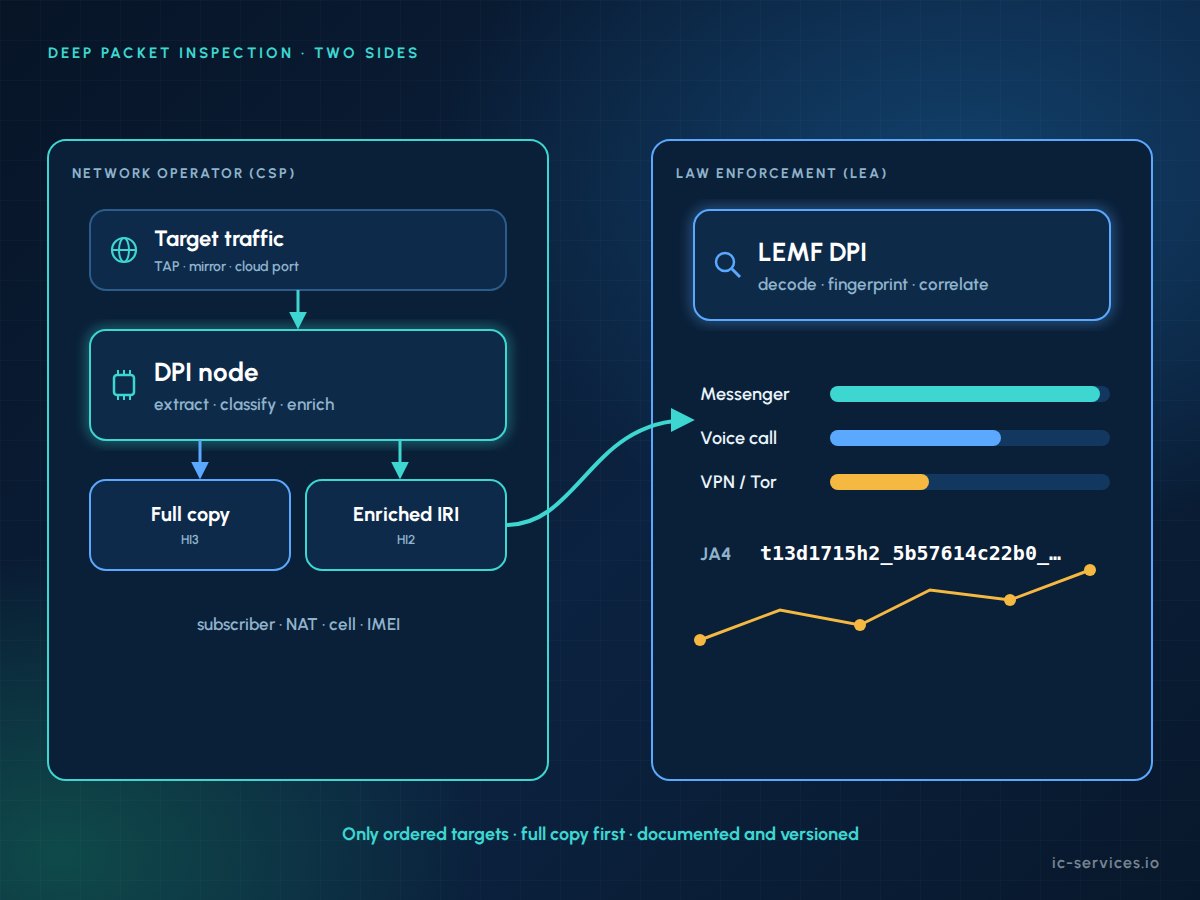
Deep packet inspection (DPI) is the analysis of network traffic beyond basic addressing, including protocol headers, handshakes, payloads and traffic patterns. In DPI lawful interception, it is applied only to the traffic of an ordered target. It runs either in the agency’s monitoring facility or at the operator’s point of interception.
Datos clave
- Two places: agency-side DPI in the LEMF and provider-side DPI at the point of interception.
- No decryption of end-to-end encryption: DPI classifies what it cannot read.
- Target-only: DPI lawful interception processes the ordered target’s traffic, nothing else.
- Full copy first: provider-side results are delivered in addition to the complete, unaltered copy.
- Documented: engine, signature and classifier versions are recorded for every result.
Why did encryption change deep packet inspection?
A decade ago, intercepted IP traffic could often be rebuilt into web pages, e-mails and chats. Today, TLS 1.3, QUIC, end-to-end encrypted messengers, VPNs and encrypted DNS hide most content. See our article on encrypted DNS and lawful interception.
Content decoding alone no longer delivers results. Deep packet inspection fills the gap. It identifies the application, fingerprints the client, recognizes activity types such as messages or calls, and correlates traffic with network context.
The two sides of DPI lawful interception
ICS supports DPI on both sides of the handover interface.
01
DPI for law enforcement
Agencies decode readable traffic and classify encrypted traffic with TLS fingerprinting, pattern recognition and IP correlation. Más información
02
DPI for network operators
Operators extract and enrich metadata for the ordered target and deliver it with the full copy. Más información
03
Built into ICS LEMF
DPI, timelines, maps and graphs are part of the ICS LEMF analyst workbench. Más información
04
Delivered through mediation
Provider-side results reach agencies through the ICS mediation and handover chain. Más información
LEA-side vs CSP-side deep packet inspection
| Aspecto | LEA-side DPI | CSP-side DPI |
|---|---|---|
| Where it runs | In the agency’s LEMF | At the operator’s point of interception |
| Input | Delivered HI2 and HI3 data | Live traffic of the ordered target |
| Output | Decoded products, classifications, timelines, graphs | Extracted metadata and enriched IRI, plus the full copy |
| Context available | Delivered IRI, case data, other targets | Subscriber, NAT mapping, cell, device identifiers |
| Legal basis and limits | Interception order, criminal procedure law, Directive (EU) 2016/680 | Interception order, national LI rules (in Germany § 170 TKG, TKÜV), Regulation (EU) 2015/2120 |
| Typical users | Analysts and investigators | MNOs, MVNOs, ISPs and their LI teams |
Where are the legal boundaries?
DPI in lawful interception is lawful only within clear limits. These apply on both sides:
- Processing stays within the scope of the order and covers only the ordered target.
- Operators deliver the complete, unaltered copy first. Enrichment is an addition.
- LI processing is strictly separated from commercial DPI and traffic management under Regulation (EU) 2015/2120.
- Agencies process data under national criminal procedure law and Directive (EU) 2016/680.
- In Germany, provider-side deliveries must be part of the concept accepted by the BNetzA under the TKÜV and TR TKÜV.
- Classifications are indicators with known error rates, not proof.
¿Por qué ICS?
01
Both sides of the handover
We operate interception for providers and build ICS LEMF for agencies, so we know what DPI can deliver on each side.
02
Regulatory experience
More than 20 years in lawful interception and multiple BNetzA acceptances for interception solutions.
03
Hands-on IP expertise
Our team works with VoLTE, IMS and IP traces and develops custom decoders and classifiers.
Preguntas frecuentes
What is deep packet inspection in lawful interception?
Deep packet inspection in lawful interception is the analysis of an ordered target’s intercepted traffic beyond addresses and ports. It decodes readable protocols and classifies encrypted traffic by application, fingerprint and activity type. It runs in the agency’s monitoring facility or at the operator’s point of interception, always within the scope of the interception order.
Can DPI decrypt encrypted messenger traffic?
No. DPI does not break end-to-end encryption. It can show that a messenger was used, when, for how long and with how much data, and often whether the activity was a message or a call. Operators only remove encryption they applied themselves in their own network.
Does provider-side DPI replace the full copy?
No. In Germany and many other jurisdictions, the operator must deliver a complete, unaltered copy of the target’s communication, unless the order explicitly limits the scope. DPI results are only delivered in addition. Agencies can therefore verify enriched data against the original traffic at any time.
Is DPI for lawful interception compatible with net neutrality rules?
Yes, if it is set up correctly. Regulation (EU) 2015/2120 restricts DPI for traffic management but allows measures required to comply with Union or national law. LI processing must therefore run separately from commercial DPI and must never feed commercial systems.
Which side should run DPI?
Often both. Agency-side DPI gives analysts flexible classification and correlation across a whole case. Provider-side DPI adds network context that only the operator has, such as subscriber, NAT and cell data. The right split depends on national rules, the operator’s acceptance concept and the agencies’ requirements.
Plan your DPI approach with ICS
Whether you analyze intercepts or deliver them, we help you design DPI that is useful, lawful and documented.