בדיקת תוכן מעמיקה של מנות נתונים לצורך יירוט חוקי נוטה להיות מזוהה עם תחום אכיפת החוק: הסוכנות מקבלת מנות IP גולמיות ומנתחת אותן במתקן הניטור שלה. עם זאת, יותר ויותר מפעילי רשתות וסוכנויות שואלים אם ניתן לבצע חלק מהעבודה הזו אצל הספק, קרוב לתעבורה. במודל זה, הספק מחלץ ומעשיר את המטא-נתונים בנקודת היירוט ומעביר אותם יחד עם העותק המלא של התקשורת.
Whether a provider may do any of this depends on national law: in Germany, analysis stays with the agency. Where it is allowed and done right, provider-side DPI speeds up investigations, can reduce data volumes where an order limits the scope, and gives agencies context they could not reconstruct themselves. Done wrong, it breaks evidence rules or exceeds the legal mandate. This article explains the architecture, what can be extracted, how enriched data is delivered, and where the boundaries are.
נקודות עיקריות
- DPI בצד הספק תוספות העותק המלא של ההודעה. הוא אינו מחליף אותה בשום אופן, אלא אם כן הצו והכללים הלאומיים מתירים במפורש היקף מצומצם יותר.
- לספק יש network context the agency lacks: line identity, NAT mappings, cell and location data, device identifiers and precise session timing. Subscriber details such as name and address need a separate request.
- נתוני מטא-נתונים אופייניים שנשלפו כוללים: רשומות זרימה, DNS, SNI, טביעות אצבע של TLS (JA4), סיווג יישומים, איתות VoIP וסוגי פעילות.
- יש לספק את הנתונים המועשרים ב- פורמט מוסכם ומתועד, for example as additional IRI records where the national specification allows it. Whether a provider may deliver any of it is jurisdiction-dependent: in Germany the provider hands over only the copy and the § 7 TKÜV event data, and analysis belongs to the agency.
- Where national law allows it, everything must be target-specific, reproducible, documented and strictly separated from commercial DPI. An acceptance concept documents it but cannot make it lawful.
מדוע יש לבצע בדיקה מעמיקה של מנות (DPI) בצד הספק?
| נהג | יתרון עבור הסוכנות | יתרון עבור הספק |
|---|---|---|
| גידול ברוחב הפס (FTTH רב-גיגה-ביט, 5G) | המטא-נתונים זמינים באופן מיידי, גם אם עיבוד העותק המלא אורך זמן | פחות לחץ על קישורי המסירה במקרים שבהם חלים מגבלות היקף |
| תעבורה מוצפנת | מפגשים וטביעות אצבעות שסווגו מראש | ניצול מחדש של הידע הקיים בתחום ה-DPI |
| הקשר הרשת | Line, NAT, cell and device data attached to each flow | Fewer follow-up requests for basic context, where national rules list the data for the copy (subscriber name and address always need a separate request) |
| מקרים דחופים | התראות כמעט בזמן אמת על דפוסי פעילות | תהליך אוטומטי המוגדר בבירור |
| מודלים מורכבים של גישה | ייחוס נכון מאחורי CGNAT ובהתקנות סיטונאיות | פחות מחלוקות בנוגע להאזנות שלא הושלמו |
היכן החוק מציב את הגבול
לפני שתתחילו לתכנן דבר כלשהו, על הספקים להבין את מעמדם המשפטי:
- הטקסט המלא מופיע ראשון. In most European jurisdictions the provider must deliver a עותק מלא, ללא שינויים of the target’s telecommunications. Where national law allows enrichment, it is an addition; in Germany it is not allowed (see below). Filtering is allowed only where the order limits the scope.
- אין ניתוח מעבר לצו. DPI בצד הספק רשאי לעבד רק את התעבורה של ה- יעד מסודר ורק לצורך היירוט. ניתוח המוני או לא ממוקד אינו מותר.
- הפרדה מ-DPI מסחרי. תקנת האיחוד האירופי בנושא האינטרנט הפתוח (EU) 2015/2120 מגבילה את השימוש ב-DPI לצורכי ניהול תעבורה, אך מתירה נקיטת אמצעים הנדרשים לצורך עמידה בחוקי האיחוד או בחוקים הלאומיים. לפיכך, עיבוד LI חייב להתבצע בסביבה נפרדת, עם בקרת גישה, ואסור בשום פנים ואופן להזין ממנו נתונים למערכות מסחריות.
- סודיות. הצוות והמערכות כפופים לחובת סודיות בתחום התקשורת, והמנויים אינם אמורים להבחין בצעד זה.
- Germany is stricter. The obliged provider must enable the measure (§ 100a(4) StPO) and hand over a complete copy plus the event data listed in § 7 TKÜV, and nothing else at the handover point (§ 8(2) No. 2 TKÜV). Analysis of the content, including DPI classification, belongs to the agency. A BNetzA acceptance cannot create a legal basis for extra processing. Provider-side enrichment is only an option where national law expressly provides for it.
ארכיטקטורת ייחוס
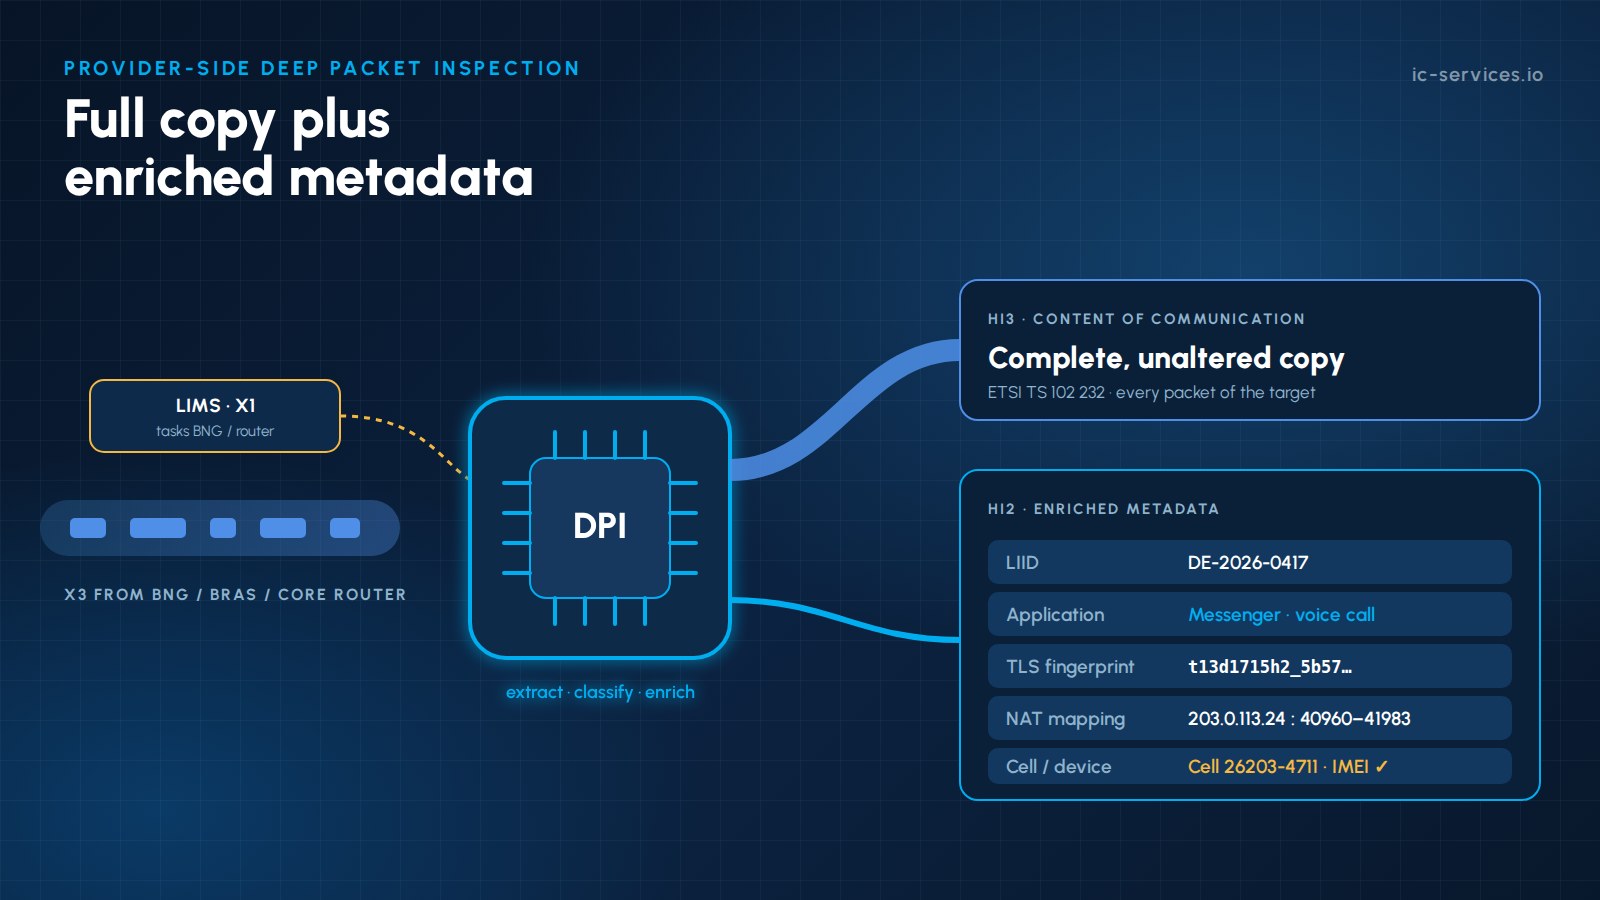
- נגישות תחבורתית: BNG/BRAS for PPPoE and IPoE access, and PE or core routers for fixed-IP lines, copy the target’s traffic with their built-in LI function, using ETSI TS 103 221 (X1 tasking, X2/X3 delivery) where supported or the vendor’s LI interface. The ADMF handles the tasking, and the mediation layer converts the delivered streams into the ETSI handover format. Optical TAPs or virtual mirror ports are only a fallback where no native LI function is available.
- הפעלת היעד: מערכת ה-LIMS/ADMF מפעילה את היעד, ואירועי הפעלה מ-RADIUS/Diameter, DHCP או משער החבילות מודיעים לצומת ה-DPI אילו כתובות IP וקידומות שייכות כרגע ליעד.
- צומת לבדיקת חבילות נתונים מעמיקה ספציפית ליעד: הצומת מעבד רק את זרם ה-X3 של היעד המסודר. הזרמים מורכבים מחדש, הפרוטוקולים מזוהים והמטא-נתונים מופקים, באמצעות עיבוד מנות בעל ביצועים גבוהים (למשל, DPDK או כרטיסי רשת מבוססי FPGA) בקצב של 10/40/100 Gbit/s.
- העשרה: each flow is tagged with the LIID, the target identifier, the NAT mapping (public IP and port block), cell ID or location, and the IMEI where available. Enrichment is limited to data the national rules list for the copy; subscriber details such as name and address still require a separate information request.
- תיווך ומסירה: the full copy is delivered as CC via HI3, according to ETSI TS 102 232-3 or -4 for fixed access, or 3GPP TS 33.108/33.128 over TS 102 232-7 for mobile, and any enriched metadata permitted by national law is delivered via HI2.
- ביקורת ושמירה: פלט ה-DPI נשמר רק כל עוד הדבר נדרש לצורך המסירה, וכל תצורה וגרסת חתימה נרשמות ביומן.
ראה ממשקי X1/X2/X3 ו- כיצד פועלת פונקציית התיווך עבור הממשקים הבסיסיים.
מה ניתן להפיק ולהעשיר?
| מטא-נתונים | מקור | הערך של החקירה |
|---|---|---|
| רשומות זרימה (חמישייה, התחלה/סיום, בתים, מנות) | כותרות מנות | סקירה מלאה של הפעילויות |
| שאילתות ותשובות DNS | DNS לא מוצפן | שירותים ודומיינים בשימוש |
| טביעות אצבע של TLS SNI, ALPN, JA4 / JA4S (שימו לב לתנאי הרישיון של FoxIO עבור JA4S) | תהליכי חיבור TLS / QUIC | זיהוי יישומים ומכשירים |
| סיווג יישומים | מאפיינים והתנהגות של DPI | מסנג'ר, VoIP, סטרימינג, VPN, Tor |
| סוג הפעילות | גודל החבילה ודפוסי התזמון | הודעה לעומת שיחה לעומת העברת קבצים |
| איתות VoIP (פרמטרים של SIP ו-RTP) | VoIP לא מוצפן | שיחות VoIP של צד שלישי – משתתפים ומשך השיחה |
| מארח HTTP וסוכן משתמש | HTTP לא מוצפן | שירותים ותוכנות לקוח |
| מיפוי NAT | יומני CGNAT | הקשר בין כתובת ה-IP הציבורית והיציאה לבין היעד |
| מיקום ומכשיר | מזהה תא, IMEI, קו גישה | היכן ובאמצעות איזה מכשיר התרחשה הפעולה |
Which of these an access provider may deliver depends on national law. In Germany, classification and service-level reconstruction of third-party services are done by the agency, not the access provider. The encryption rule applies here as well: the provider removes only the encryption it applied itself. End-to-end encrypted content remains encrypted, and the metadata above is extracted without decrypting it.
העברת נתונים מועשרים
There is no single, universal ETSI record type for “DPI results”. Flow summaries are standardised in ETSI TS 102 232-3 (Packet Data Summary Reporting); application classification is not. In practice, three models are used:
- רשומות IRI נוספות: extracted events (for example a detected VoIP call or an application session) are sent via HI2, using standard fields where possible, and national extensions only where the national specification provides for them.
- Flow-level IRI: where flow-level IRI is required by the warrant, ETSI TS 102 232-3 already defines it (Packet Data Summary Reporting, IPIRIOnly). Proprietary analytics streams outside the national handover specification are not permitted in Germany and need an explicit legal basis elsewhere.
- רשומות ברמת השירות: בחלק מהתחומים השיפוטיים, ורק כאשר הדבר נדרש במפורש, הספק מספק אירועים ברמת השירות, בדומה לחלקים הספציפיים לשירות במסמך ETSI TS 102 232, שספקי הודעות ומולטימדיה משתמשים בהם עבור השירותים שלהם.
לא משנה מהו הדגם, הפורמט חייב להיות מתועד, עם גרסאות ומוסכם עם הגופים המקבלים והרגולטור, ועל הגוף להיות מסוגל תמיד לאמת את הנתונים המועשרים מול העותק המלא.
איכות הראיות: הפיכת ההעשרה לניתנת לשחזור
- הקלט את ה- גרסת מנוע ה-DPI וגרסת החתימה משמש לכל תוצאה.
- שימוש חותמות זמן מסונכרנות ובעלות דיוק גבוה כך שהמטא-נתונים יתאימו לרישומי CC ו-HI2.
- לספק מדדי אמון לצורך סיווגים התנהגותיים.
- שמור על תיעוד ביקורת מלא של הפעלת היעד, שינויים בתצורה ומשלוחים.
- בצעו בדיקות באופן קבוע באמצעות תעבורה ייחוסית כדי לאתר רגרסיות לאחר עדכוני חתימות.
רשימת בדיקה ליישום עבור ספקים
- הערכה משפטית: מה מאפשרת המסגרת הלאומית, ומה כוללות בדרך כלל הצווים
- Where national law provides for enrichment: scope and delivery format agreed with the agencies and documented in the acceptance concept
- הפעלה ספציפית למטרה בלבד, המונעת על ידי LIMS/ADMF
- DPI המואץ בחומרה, המותאם לקצבי שיא של מנויים
- שילוב עם AAA, DHCP, יומני CGNAT, ליבת החבילות ונתוני מיקום
- הפרדה מוחלטת מ-DPI מסחרי ומניהול תעבורה
- ניהול גרסאות, בדיקות השוואה ותיעוד ביקורת
- העברה עמידה עם אגירה וניטור
כיצד ICS מסייע בבדיקת חבילות נתונים מעמיקה בצד הספק
ICS International Carrier Services builds on more than 20 years of team experience in telecommunications, lawful interception and compliance and on BNetzA-accepted LI implementations. We integrate network elements via their vendor LI interfaces or ETSI TS 103 221 X1/X2/X3 and operate mediation for providers today, so we know both the network and the receiving side.
- אדריכלות ותכנון משפטי-טכני של DPI בצד הספק (ראו DPI למפעילי רשתות) שמתאים למסגרת הלאומית שלכם ולתפיסת הקבלה שלכם.
- צינורות DPI והעשרה המופעלים על ידי יעד משולב עם RADIUS/Diameter, רישום CGNAT ואירועי ליבת החבילות.
- Network element integration with BNG/BRAS and core routers via their vendor LI interfaces or ETSI TS 103 221 X1/X3, plus passive probes or cloud mirroring where no native LI function is available.
- גישור והעברת האחריות ל-ETSI באמצעות ה- פלטפורמת הגישור LI ו- LIMS.
- תפעול מנוהל 24 שעות ביממה. ראה ניהול פעולות LI.
- פיתוח מותאם אישית של מכשירי מיצוי, מסננים ופורמטים של אספקה. ראה אינטגרציה ופיתוח מותאם אישית.
צרו קשר עם ICS כדי לדון בשאלה האם העשרת תוכן מצד הספק מתאימה לרשת שלכם.
שאלות נפוצות
האם מותר לבצע בדיקה מעמיקה של מנות נתונים (DPI) לצורך יירוט חוקי?
Only where national law expressly provides for it. In Germany the provider must hand over a complete copy plus the event data listed in § 7 TKÜV and nothing else at the handover point (§ 8(2) No. 2 TKÜV); analysis of the content, including DPI classification, belongs to the agency, and a BNetzA acceptance cannot create a legal basis for extra processing. Untargeted or commercial use of LI data is never allowed.
האם ה-DPI בצד הספק מחליף את העותק המלא של התקשורת?
לא. ברוב תחומי השיפוט, על הספק למסור עותק מלא ובלתי משונה של התקשורת של היעד. מטא-נתונים המבוססים על DPI נמסרים בנוסף לכך, אלא אם כן הצו מגביל במפורש את היקף המסירה.
האם ספק שירותי אינטרנט יכול לפענח את תעבורת ה-HTTPS או את תעבורת המסרים המיידיים של היעד?
לא. הספק מסיר רק את ההצפנה שהוא עצמו יישם ברשת שלו. ההצפנה מקצה לקצה או ברמת היישום נשארת על כנה. טכנולוגיית DPI פועלת על כותרות, תהליכי חיבור ודפוסי תעבורה שאינם מוצפנים.
כיצד מועברים נתוני ה-DPI לרשויות אכיפת החוק?
Where national law allows it, as additional IRI records via HI2, using standard records such as the Packet Data Summary Reporting of ETSI TS 102 232-3 where possible. Separate analytics streams outside the national handover specification are not permitted in Germany. The format must be documented and agreed with the agencies and the regulator.
מה ההבדל בין DPI בצד הספק ל-DPI בצד הרשות המקומית לחינוך (LEA)?
LEA-side DPI analyses the delivered traffic in the monitoring facility. Provider-side DPI runs at the point of interception, where, if national law allows it, it can add network context such as the line identifier, NAT mappings and location, and deliver results in near real time.
מאמרים קשורים
- כיצד פועלת פונקציית הגישור: הגשר בין הרשת שלכם לבין רשויות אכיפת החוק
- DNS מוצפן (DoH/DoT) והשפעתו על יכולות היירוט החוקיות
- חיתוך רשת ב-5G SA: כיצד הדבר מסבך (ויכול לפשט) את מיקוד ה-LI
- LI בסיוע בינה מלאכותית: מה משמעות האוטומציה עבור המפעילים ותהליכי העבודה של רשויות אכיפת החוק