
ENCRYPTED TRAFFIC ANALYSIS
DPI for Law Enforcement: Making Encrypted Intercepts Usable
Identify apps, devices and activities in encrypted IP intercepts with TLS fingerprinting, traffic pattern recognition and correlation, inside the ICS LEMF analyst workbench.
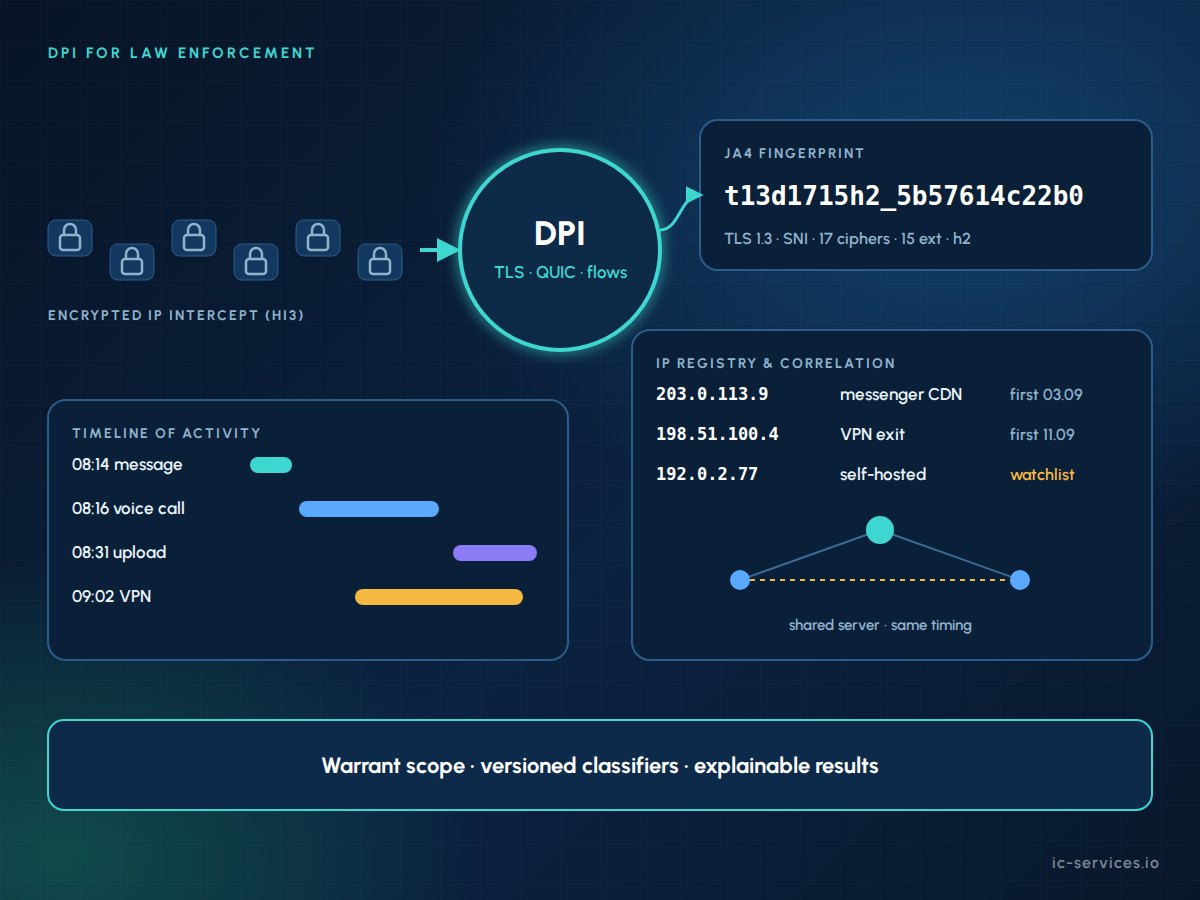
DPI for law enforcement is deep packet inspection of lawfully intercepted IP traffic inside the agency’s monitoring facility. It decodes what is still readable and classifies what is encrypted, using TLS fingerprinting, traffic pattern recognition and IP correlation. It does not break end-to-end encryption.
Dati salienti
- Two jobs: decode readable traffic, classify everything else.
- TLS fingerprinting: JA4 identifies client software from the handshake without decryption.
- Pattern recognition: packet sizes and timing reveal messages, calls and file transfers.
- Correlation: an IP registry links activity across targets, devices and time.
- Evidential discipline: versioned classifiers, known error rates, warrant scope enforced.
- Available in ICS LEMF for agencies.
Why does DPI for law enforcement matter now?
When an operator delivers a target’s internet traffic, almost all of it is encrypted. HTTPS, QUIC, end-to-end encrypted messengers, VPNs and DNS over HTTPS leave little content to decode. A monitoring facility that only shows gigabytes of TLS gives investigators nothing to work with.
Encrypted traffic analysis changes that. Even without content, traffic shows which application was used, when, how intensively and alongside which other activities. Analysts expect continuously updated classifiers, and they want to adjust the rules themselves.
What can encrypted traffic analysis still see?
| Signal | What it reveals | Limitations |
|---|---|---|
| IP addresses, ports, ASN | Server infrastructure, cloud or CDN, VPN endpoints | Shared CDN addresses serve many services |
| DNS (unencrypted) | Domains the target looked up | Hidden by DoH and DoT |
| TLS SNI | Requested server name | Can be hidden or misleading |
| TLS version, ciphers, ALPN | Client type and protocol stack | Needs fingerprinting to interpret |
| Server certificate | Organization, domain, issuer | Encrypted in TLS 1.3 |
| QUIC Initial packets | Server name and client parameters | Later packets fully encrypted |
| Packet sizes and timing | Message, call, video or file transfer | Needs trained models |
| Flow volume and duration | Usage intensity and daily patterns | Needs context to interpret |
| STUN/TURN traffic | Real-time calls and peer-to-peer media | App-specific |
For the impact of encrypted DNS, read DoH, DoT and lawful interception.
TLS fingerprinting: JA3 vs JA4
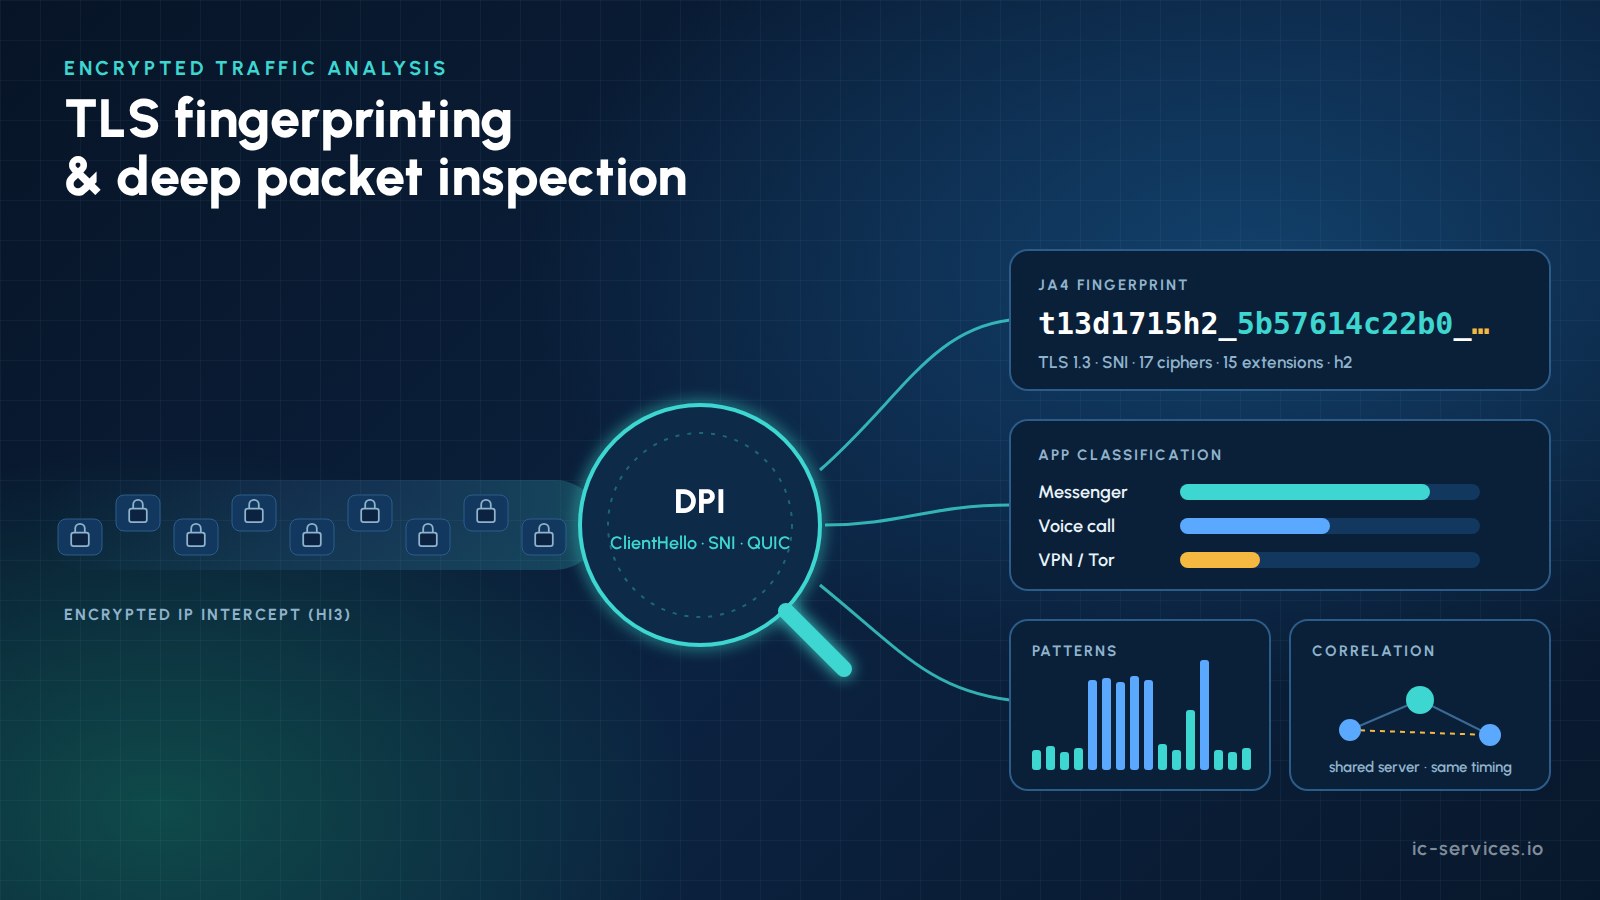
Every TLS client builds its ClientHello in a characteristic way. TLS fingerprinting condenses version, cipher suites, extensions and ALPN values into a short, comparable string. It identifies apps, browsers, libraries and tools without decrypting anything.
| Method | Approach | Practical note |
|---|---|---|
| JA3 | MD5 hash of ClientHello fields in the order sent | Breaks when browsers randomize extension order |
| JA4 | Sorted values plus a readable prefix (transport, TLS version, SNI, counts, ALPN) | Stable despite randomization; BSD 3-Clause license |
| JA4S, JA4H, JA4X, JA4L, JA4SSH | Server, HTTP, certificate, latency and SSH fingerprints | FoxIO License 1.1; commercial products need an OEM license |
JA4 is widely adopted as the successor to JA3. Vendors and buyers should check the license terms before using other JA4+ methods in a commercial product. A fingerprint is a strong indicator, not proof of identity, because many apps share common libraries.
How does traffic pattern recognition work?
Even when content and server names are hidden, the shape of the traffic remains visible:
- Text messages appear as short bursts of small packets, followed by receipts.
- Voice and video calls create steady, evenly spaced UDP streams, often after a STUN/TURN exchange.
- File and media transfers show sustained high-volume uploads or downloads.
- Keep-alives and push notifications follow app-specific rhythms.
Classifiers trained on packet lengths, inter-arrival times and burst statistics label these activities. The analyst sees an event timeline, for example a message at 08:14 followed by a voice call at 08:16.
IP registry and correlation
Classification becomes intelligence once it is correlated. ICS LEMF keeps an IP registry per case and across cases.
- IP-to-service resolution with ASN, reverse DNS, certificate data and geolocation.
- First seen and last seen for every remote address and fingerprint.
- Watch lists of addresses, domains and fingerprints that trigger alerts.
- Common contact points between targets, such as the same rare server or VPN endpoint.
- Temporal correlation of activity that starts and stops at the same time on two lines.
- Device continuity when identical fingerprints appear on different SIM cards.
- IRI linkage with cell IDs, locations and IMEIs.
Public IP addresses seen in third-party data can lead to a subscriber through a subscriber data request to the access provider under § 174 TKG. The planned German rules on IP address retention (§ 177 TKG-E, BT-Drs. 21/6581, currently in parliament) are designed to support this. Learn more about data retention and IP retention.
How DPI for law enforcement works in ICS LEMF
Every result follows a documented chain from raw packets to the analyst workbench.
1
Ingest
HI3 IP deliveries (ETSI TS 102 232-3 for internet access, -7 for mobile) arrive with the matching HI2 records.
2
Sessionize
Packets are grouped into flows and sessions, even across IP address changes.
3
Decode
Web, e-mail, file transfers and VoIP become readable products.
4
Classify
DPI signatures, JA4 fingerprints and behavioral models label the remaining traffic.
5
Enrich
The IP registry adds service, geolocation and IRI context.
6
Correlate
Activity is linked across targets, cases and time.
7
Visualize and alert
Timelines, maps and graphs, with drill-down to the raw PCAP.
8
Document
Decoder and classifier versions are stored with every result.
What are the legal and evidential boundaries?
DPI for law enforcement operates under strict limits. ICS LEMF enforces them technically wherever possible.
- Analysis stays within the scope of the warrant and the measures an analyst is authorized for.
- Every processing step follows national criminal procedure law and Direttiva (UE) 2016/680.
- Le classificazioni sono indicatori. Their error rates must be known, documented and explainable in court.
- Versioning keeps the original result visible when data is re-analyzed with a newer classifier.
- Privileged content can be flagged and locked, subject to administrator approval.
DPI capabilities in ICS LEMF
All analysis functions work within the analyst’s authorized measures.
01
Protocol decoding
Web sessions, e-mail (POP3, IMAP, SMTP), VoIP and file transfers are rebuilt as products, with OCR and metadata extraction.
02
App classification
Continuously updated DPI signatures show which service was used, when and with how much data. Agencies can adjust rules themselves.
03
TLS fingerprinting
JA4-based client fingerprints identify apps, browsers and tools, with watch lists for fingerprints of interest.
04
Activity recognition
Behavioral models distinguish messages, calls and transfers inside encrypted apps and place them on the case timeline.
05
Timelines, maps and graphs
All events on one second-accurate timeline, locations on maps and relationships in entity graphs, with geofence alerts.
06
Open analysis chain
PCAP export to Wireshark and a decoder plugin API let your team add protocols and use its own tools.
Perché ICS
01
Provider-side insight
We run interception for operators, so we know what IP deliveries look like and where they break.
02
Standards and regulation
Oltre 20 anni di esperienza nel settore delle intercettazioni legali e numerose certificazioni rilasciate dalla BNetzA per soluzioni di intercettazione.
03
Custom classifiers
Our developers build decoders, classifiers and enrichment pipelines to your requirements. Per saperne di più
Domande frequenti
What is DPI for law enforcement?
DPI for law enforcement is deep packet inspection of IP traffic that an agency receives through lawful interception. Inside the monitoring facility, it decodes readable protocols and classifies encrypted traffic by application, fingerprint and activity type. Results are correlated with IRI, locations and other targets, and every step stays within the scope of the interception order.
What is TLS fingerprinting?
TLS fingerprinting derives a compact identifier from the parameters a client or server uses in the TLS handshake, such as version, cipher suites, extensions and ALPN values. It identifies the software behind a connection, for example a specific messenger, browser or tool, without decrypting the traffic. It is an indicator and should be combined with other signals.
What is the difference between JA3 and JA4?
JA3 hashes ClientHello fields in the order they appear. Since browsers randomize extension order, the same browser now produces many different JA3 hashes. JA4 sorts the values before hashing and adds a readable prefix, so the fingerprint stays stable. JA4 is published under the BSD 3-Clause license, while the other JA4+ methods use the FoxIO License 1.1.
Can DPI decrypt WhatsApp or Signal traffic?
No. DPI does not break end-to-end encryption. It can show that such an app was used, when, for how long and with how much data. Traffic pattern recognition can often tell a text message from a voice call. Access to content requires other legal instruments and is not part of DPI.
Is encrypted traffic analysis lawful for agencies?
It is lawful when a valid interception order covers the traffic. The analysis must follow national criminal procedure law and data protection rules, in the EU, Directive (EU) 2016/680. Analysis must stay within the scope of the order. Results must be documented and versioned, and privileged communications must be protected.
What is an IP registry?
An IP registry is a database of remote IP addresses, domains and fingerprints observed in intercepted traffic, kept per case and across cases. It adds service, ASN and geolocation data and records when each item was first and last seen. In ICS LEMF, it is the basis for correlation, watch lists and alerts.
See encrypted traffic analysis in ICS LEMF
Book a demo and see how DPI, TLS fingerprinting and correlation work on intercepted IP data.